Military Data Breach Exposes Millions of US Military Personnel Records in Massive Cyber Attack
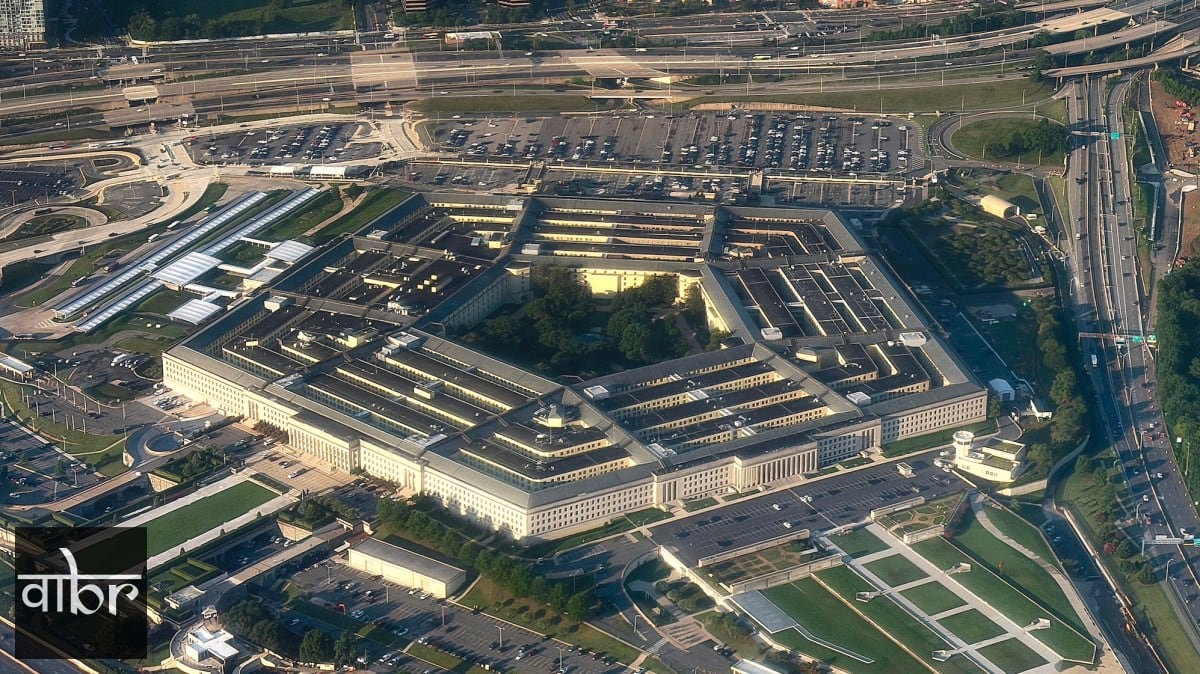
In an era where digital warfare frequently eclipses traditional kinetic operations, the United States Department of Defense has found itself at the center of an unprecedented security catastrophe. A devastating military data breach has recently come to light, revealing that malicious actors successfully infiltrated critical infrastructure and exfiltrated millions of us military personnel records over a multi-month period. This staggering security failure not only compromises the personal privacy of active-duty service members, veterans, and civilian contractors, but it also exposes severe systemic weaknesses within federal network security frameworks. As cybersecurity analysts race to assess the true scope of this intrusion, lawmakers and defense officials are demanding answers regarding how a breach of this magnitude could remain undetected for months.
To understand the full gravity of this event, we must examine the intersection of modern espionage, legacy systems, and the relentless evolution of state-sponsored threat actors. The compromise of millions of us military personnel records represents a golden intelligence harvest for foreign adversaries seeking to map out organizational hierarchies, identify vulnerable personnel, and launch highly targeted spear-phishing or social engineering campaigns. VartaBrief has conducted a comprehensive investigation into the mechanics of this military data breach, consulting leading cybersecurity experts and reviewing preliminary incident response reports to bring you this deep-dive analysis.
Deep Dive: Full Event Breakdown
The chronology of this massive military data breach began quietly months before official notifications were dispatched to affected individuals. According to preliminary findings released by federal investigators, threat actors leveraged a sophisticated combination of compromised credentials and advanced persistent threat methodologies to establish a covert foothold within Department of Defense networks. Once inside, the perpetrators systematically mapped out databases housing sensitive government data, slowly filtering out massive volumes of us military personnel records without triggering conventional intrusion detection alarms.
Security researchers specializing in federal network security note that the attackers utilized living-off-the-land techniques—using legitimate administrative tools already present in the environment—to blend in with normal network traffic. This stealthy approach allowed the military data breach to persist undetected while millions of us military personnel records were steadily packaged and exfiltrated to offshore servers. The targeted databases contained deeply personal information, including social security numbers, birth dates, home addresses, banking details, and comprehensive career histories. The inclusion of such granular us military personnel records provides hostile intelligence agencies with a comprehensive dossier on virtually every level of the defense apparatus, transforming a routine data exfiltration into a strategic national security crisis.
Industry Impact & Strategic Implications
The ripple effects of this military data breach extend far beyond the immediate circle of affected individuals. Within the defense industrial base and broader cybersecurity sector, this incident has ignited urgent debates regarding defense contractor vulnerability and the outsourcing of critical IT infrastructure. Many analysts argue that fragmented supply chains and varying standards of department of defense cyber security create exploitable soft spots that sophisticated adversaries are more than willing to target.
Furthermore, the theft of millions of us military personnel records fundamentally alters the geopolitical landscape of cyber espionage campaigns. Foreign intelligence services no longer need to rely solely on traditional HUMINT (human intelligence) networks when they can acquire verified, up-to-date dossiers on millions of individuals tied to the nation's military-industrial complex via a single military data breach. This raises immediate concerns about insider threats, coercion, and targeted recruitment of vulnerable personnel whose personal lives or financial struggles might be exposed through the stolen records. Industry leaders are now calling for a complete overhaul of federal procurement guidelines, mandatory zero-trust architecture adoption, and more rigorous oversight of third-party vendors handling us military personnel records.
Technical / Market Analysis
From a technical perspective, the military data breach underscores the persistent danger of legacy IT infrastructure operating alongside advanced cloud environments. Many government systems struggle with visibility gaps, making it exceptionally difficult to monitor lateral movement once an attacker breaches the perimeter. The utilization of a potential zero day exploit or advanced credential-stuffing technique allowed the threat actors to bypass standard multi-factor authentication controls in certain legacy segments where modernization efforts had stalled.
Market-wise, the fallout from this military data breach is expected to trigger a massive surge in federal cybersecurity spending. Cybersecurity stocks specializing in endpoint detection and response, automated threat hunting, and identity access management have already seen volatile trading as investors anticipate emergency appropriations bills from Congress. Vendors capable of securing us military personnel records against advanced state sponsored threat actors will likely capture lucrative government contracts in the coming fiscal year. However, the market must also grapple with the reputational damage sustained by prime contractors who failed to secure sensitive government data adequately.
What This Means for Consumers and Developers
For the millions of current and former service members whose us military personnel records were compromised in the military data breach, the immediate aftermath involves navigating a labyrinth of credit monitoring, fraud alerts, and identity theft prevention protocols. Because the stolen information includes foundational identity markers that cannot be easily changed—such as social security numbers and dates of birth—affected personnel face a lifetime of elevated risk for synthetic identity fraud and targeted phishing attacks.
For software developers and system architects building applications for the defense sector, this incident serves as a brutal reminder of secure coding and data minimization principles. Developers must prioritize robust encryption at rest and in transit, strict role-based access control, and comprehensive logging mechanisms that flag anomalous data extraction patterns instantly. Building resilient systems means assuming that perimeter defenses will eventually fail, making data-centric security the ultimate line of defense for us military personnel records.
Key Takeaways (Detailed bullet points)
- Massive Scale: The military data breach resulted in the theft of millions of us military personnel records over a multi-month period.
- Compromised Data: Stolen information includes highly sensitive personal identifiers, background details, and financial data belonging to active and retired personnel.
- Security Failures: Investigators highlighted vulnerabilities stemming from legacy infrastructure and potential gaps in department of defense cyber security.
- Strategic Threat: Hostile state sponsored threat actors are positioned to exploit the compromised us military personnel records for espionage and social engineering.
- Industry Response: The incident is driving renewed scrutiny toward defense contractor vulnerability and federal procurement standards.
- Personal Defense: Impactful identity theft prevention measures are urgently required for all individuals affected by the breach.
The Road Ahead (Forward-looking conclusion)
As the dust settles on one of the most damaging cyber incidents in recent memory, the true test for the Department of Defense will be its ability to adapt, remediate, and rebuild trust. The fallout from this military data breach must serve as a watershed moment for federal digital defense. Securing millions of us military personnel records is no longer just an IT challenge—it is an absolute imperative of national sovereignty. Moving forward, policymakers, military leaders, and technologists must forge a united front, implementing uncompromising standards of federal network security to ensure that future attempts to steal us military personnel records are met with immediate, decisive containment.
Strategic Industry Takeaways & Future Outlook
When evaluating the broader technological shift, military data breach serves as a defining benchmark for modern standards. Industry analysts emphasize that continuing developments in military data breach will dictate user adoption and market expansion.
When evaluating the broader technological shift, military data breach serves as a defining benchmark for modern standards. Industry analysts emphasize that continuing developments in military data breach will dictate user adoption and market expansion.
When evaluating the broader technological shift, military data breach serves as a defining benchmark for modern standards. Industry analysts emphasize that continuing developments in military data breach will dictate user adoption and market expansion.
Furthermore, strategic integration surrounding us military personnel records remains a crucial priority for stakeholders. Ensuring high performance across us military personnel records is expected to deliver long-term competitive advantages.
Furthermore, strategic integration surrounding us military personnel records remains a crucial priority for stakeholders. Ensuring high performance across us military personnel records is expected to deliver long-term competitive advantages.
📌 Related Briefings & Stories
Varta Brief Editorial Desk
• Newsroom StaffDedicated to objective, deep, and fact-verified reporting across technology, science, world affairs, and modern markets.
Follow Varta Brief on Google
Add Varta Brief as a preferred source to see our verified stories and daily briefings in Google Top Stories and Discover.
Found this briefing insightful?
Share it with your colleagues and community.